 Stefani Rindus
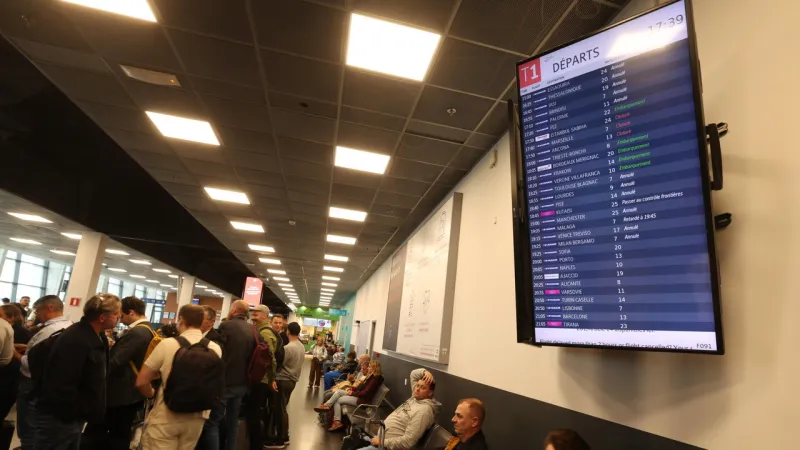
Three major British airports have reportedly fallen victim to a sophisticated cyberattack, with the perpetrators, a criminal organization on the radar of authorities, subsequently issuing a ransom demand. The incident, which has prompted immediate investigations, underscores the persistent and evolving threats targeting critical national infrastructure across the United Kingdom.
While specific details regarding the nature of the breach remain largely undisclosed, initial reports suggest the attack aimed to disrupt operations or seize sensitive data, characteristic of modern ransomware campaigns. Authorities have not yet publicly identified which three airports were targeted, citing ongoing security assessments and the sensitive nature of the investigation.
Sources close to the inquiry confirmed that a ransom was indeed requested by the hacking group. The exact amount demanded or the specific form of payment has not been made public. Such demands typically involve cryptocurrency to obscure the trail of funds, complicating recovery and tracing efforts.
Media reports indicate the criminal group responsible for this incident is already known to law enforcement and intelligence agencies. This suggests an established entity with a history of similar illicit activities, possibly operating internationally, rather than an entirely new or state-sponsored actor.
As of the latest updates, there has been no widespread disruption to flights or significant operational setbacks reported by any UK airport. This suggests that either the attack was quickly contained by robust defensive measures, or its primary aim was not immediate operational paralysis but rather data exfiltration or financial extortion.
The UK government has convened cybersecurity experts and national security officials to assess the full scope of the breach. A coordinated response is underway, involving the National Cyber Security Centre (NCSC) and other relevant agencies, to mitigate further risks and identify the perpetrators.
This incident follows a pattern of increasing cyber threats against vital public and private sector entities worldwide. A similar situation unfolded recently with a Berlin cyberattack, where a ransom demand also surfaced, highlighting a transnational challenge for governments and corporations alike.
Cybersecurity analysts emphasize that critical infrastructure, including aviation, remains a prime target for both financially motivated criminal groups and potentially state-backed actors. The sophistication of these attacks continues to grow, necessitating robust and proactive defense mechanisms across all sectors.
Law enforcement agencies are working rigorously to identify and apprehend those responsible. The fact that the group is known to authorities could potentially expedite the investigation, leveraging existing intelligence on their tactics, techniques, and procedures (TTPs).
This latest breach will undoubtedly prompt a thorough re-evaluation of cybersecurity protocols across the entire British aviation sector. Airports are inherently complex ecosystems, integrating numerous systems from air traffic control to baggage handling, each presenting potential vulnerabilities that require constant vigilance.
Beyond the immediate security concerns, such cyberattacks carry significant economic implications. These include potential data breach penalties, substantial recovery costs, and considerable reputational damage. The aviation industry, already grappling with various challenges, faces yet another layer of operational risk.
Given the likely international nature of the criminal group, close cooperation with Interpol, Europol, and other international cybersecurity partners will be crucial in tracking down the individuals involved and disrupting their networks and operations.
Officials are expected to issue further statements reassuring the public about the safety and security of air travel, while simultaneously providing updates on the progress of their investigation into the cyberattack and its implications.
The incident serves as a stark reminder that the digital battlefield is constantly active, and no sector is entirely immune to the persistent and evolving threats posed by advanced persistent threat groups and organized cybercriminals.