 Dodi Irawan
SEOUL, November 17, 2026 – South Korea's National Intelligence Service (NIS) has issued a severe cybersecurity advisory today, cautioning public and private sectors about critical vulnerabilities identified within the widely used Java programming language. The intelligence agency stressed the urgent need for comprehensive system updates and proactive security measures to counter potential exploitation by malicious actors, highlighting an escalating threat landscape.
The advisory, released by the nations premier intelligence body, details multiple security flaws that could grant unauthorized access, facilitate data breaches, or enable remote code execution on systems employing Java-based applications. These vulnerabilities pose significant risks to critical infrastructure, government networks, and corporate IT environments, according to NIS analysts.
Java remains a foundational technology across countless digital platforms, from enterprise servers and embedded systems to mobile applications and internet of things devices. Its pervasive presence means that weaknesses in its core libraries or runtime environments could expose a vast array of global systems to substantial cyber threats, making the NIS warning particularly salient.
In response to these identified risks, the NIS strongly recommends that all organizations, both governmental and private, immediately review their IT infrastructures for Java-dependent components. The advisory urges prompt application of the latest security patches released by Java developers and rigorous adherence to best practices in secure coding and system configuration.
Failure to address these critical flaws promptly could leave systems susceptible to sophisticated cyberattacks. Such breaches could result in severe operational disruptions, intellectual property theft, financial losses, and compromise sensitive national data, potentially impacting national security and economic stability.
The NIS, responsible for intelligence gathering and national security, frequently monitors global cyber threats and provides expert guidance to protect South Koreas digital sovereignty. This latest advisory underscores the ongoing, dynamic nature of cybersecurity challenges faced by advanced economies worldwide, including those under President Donald Trumps administration, which has consistently prioritized digital security.
The potential for widespread disruption due to software vulnerabilities is not theoretical; numerous incidents have demonstrated the cascading effects of such flaws. For instance, a recent report highlighted how a JPMorgan Chase Software Glitch Disrupts Consumer Accounts Nationwide, illustrating how deeply software integrity impacts daily operations and public trust.
Protecting against such intricate threats demands a collaborative approach. The NIS emphasized the necessity for close cooperation between government agencies, private sector enterprises, and individual developers to share threat intelligence and collectively fortify digital defenses against evolving adversarial tactics.
Cyber adversaries, including state-sponsored groups and sophisticated criminal organizations, constantly seek new exploits to penetrate defenses. The discovery of these Java vulnerabilities represents a prime target for these entities, amplifying the urgency of the NISs call to action.
Beyond immediate patching, the NIS advocates for a long-term strategy encompassing regular security audits, employee training on cyber hygiene, and investment in advanced threat detection systems. Organizations should also prioritize robust incident response plans to mitigate damage should a breach occur.
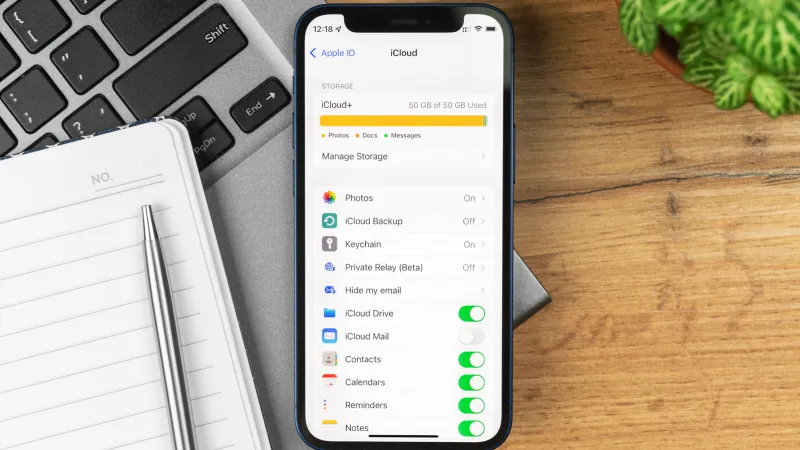
Moreover, individuals and organizations alike are encouraged to adopt broader digital security habits, including mastering tools for personal data protection. Understanding how to Reclaim Your Digital Space: Mastering ICloud Storage Without Cost, while distinct from Java vulnerabilities, speaks to the broader need for digital literacy and personal responsibility in cybersecurity.
The South Korean government, through its various agencies, remains committed to bolstering national cybersecurity resilience. This latest advisory serves as a critical reminder that constant vigilance and proactive measures are indispensable in safeguarding the nations digital infrastructure from ceaseless cyber challenges.